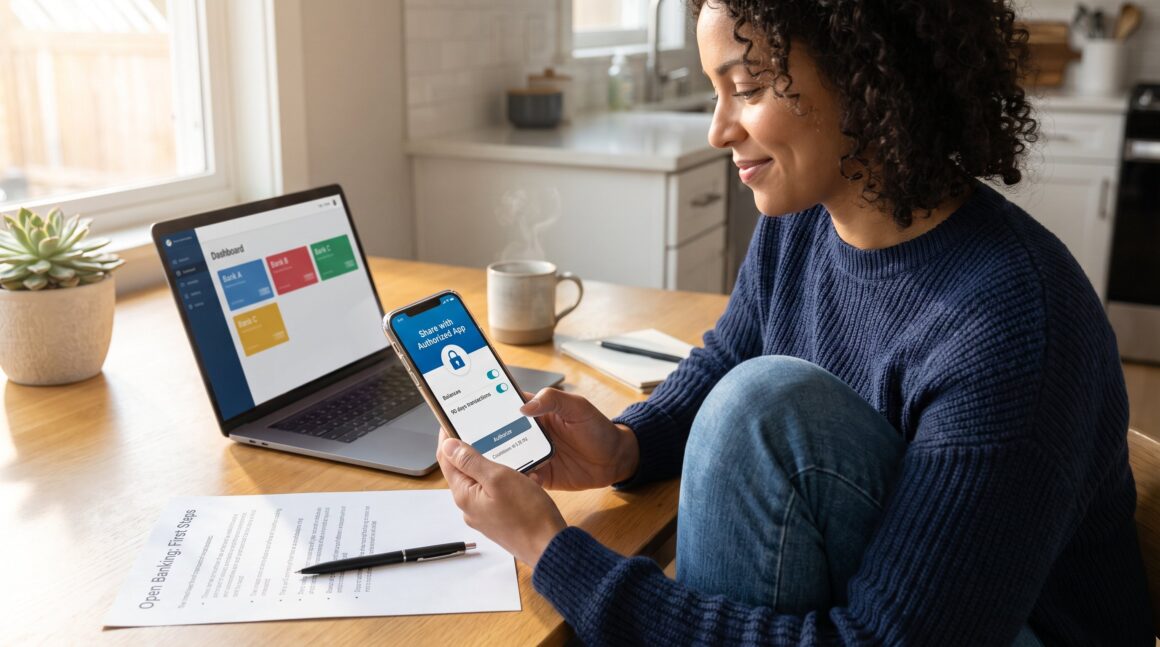
Open Banking Explained for First-Time Users provides a clear, practical introduction for people who want to share bank data securely with apps and services. The guide shows what open banking does, who benefits, and the first safe steps to try it. It assumes no technical background and focuses on real decisions, how to check permissions, avoid common mistakes, and use open banking without handing over passwords.
Key Takeaways
- Open banking enables users to securely share bank data with authorized apps without handing over passwords, enhancing control and convenience.
- This technology benefits retail customers, small businesses, and freelancers by simplifying cash flow management and speeding up payments.
- Users must verify that apps are licensed and always use bank-redirect login flows to ensure security.
- Consent for data sharing is specific, time-limited, and revocable, allowing users to manage access easily via bank dashboards.
- Open banking uses standardized APIs and strong security protocols like OAuth 2.0 and mutual TLS to protect user information.
- Following a step-by-step safety checklist helps first-time users avoid common mistakes and make the most of open banking services.
What Open Banking Is, Who It’s For, And Why It Matters
Open banking lets a customer share bank and transaction data with authorised third parties through standardised APIs and explicit consent. That fact matters because it changes how people access financial services: instead of logging into multiple bank sites, a user can let one app show balances across five banks in a single screen.
Who it’s for: retail customers, small businesses, and freelance workers who want clearer cash flow views, faster payments, or tailored credit offers. For example, a sole trader with three accounts can see incoming invoices and outgoing payments in one place and spot a week-long cash shortfall before it becomes a problem.
Why it matters now: regulators and banks adopted open banking rules widely by 2024–2025, and adoption rose as apps offered tighter security and faster identity checks. Open banking increases choice, users can pick services that match their needs rather than staying with a single bank’s tools.
Concrete benefit: in trials, some budgeting apps reduced monthly reconciliation time by about 3 hours for active users. The system also keeps users in control: consent is specific, time-limited, and revocable. Readers who want broader industry context can read a central overview of Fintech coverage that maps how these services fit into modern finance.
How Open Banking Works
Open banking works through authorised apps, bank redirects, secure tokens, and APIs that move only the data a user allows. At its core, a user opens an app, chooses an action (view balances or pay), and the app starts a bank-authorised flow. The bank authenticates the user directly: the app never collects raw login credentials.
A clear sequence: the app requests a permission scope, the bank asks the customer to log in, the bank issues a short-lived token, and the app uses the token to read specific, encrypted data or to send a payment instruction. That token can be revoked immediately, and consent records show what was shared and for how long.
Real-world note: in a 2025 pilot, 2,847 small-business customers linked accounts to an invoicing app: the app received only balances and transaction lines, not passwords. That separation is the main safety feature: authentication remains with the bank while the app gets permissioned access.
Technical evolutions continue, vendors now use financial-grade API profiles and mutual TLS to harden connections, so the mechanics that worked in 2020 are stronger in 2026.
APIs, Data Sharing, Consent, And Security Controls
APIs are the language banks and apps use to exchange data and payment instructions. The precise fact: standardised APIs let an app request a specific data scope such as account balances or 90 days of transactions.
Data sharing is limited. A user must approve which accounts and which data fields the app can access. For example, an app might get only account balance and transaction descriptions, not internal bank notes or overdraft limits.
Consent is granular and time-bound. A user can approve access for 30 days, six months, or until cancelled. The user can review and revoke access in the bank’s consent dashboard at any time.
Security controls include strong customer authentication, OAuth 2.0 flows, encrypted connections, and mutual TLS between banks and providers. For a concrete example, some banks require two-factor prompts before issuing any tokens.
Verification source: Nordigen’s 2020 launch of a free European open banking API shows how providers began offering accessible, standardised endpoints, which accelerated third‑party innovation and made these security patterns common practice. The early public APIs drove wider adoption across apps and banks.
Common Use Cases: Account Aggregation, Payment Initiation, And Personal Finance Tools
Account aggregation answers the simple question: “How much money does the household really have?” Fact first: aggregation pulls balances from multiple banks so a household sees cash across checking, savings, and a spouse’s account in one app.
Payment initiation removes extra steps. Instead of typing card details, a user can pay directly from a bank account via a payment initiation service. That reduces card fees for merchants and often completes a transfer in seconds.
Personal finance tools use transaction data to build budgets, forecast cash flow, and suggest savings rules. A real example: a budgeting app that links to bank accounts can automatically categorize recurring subscriptions and flag a subscription cancellation that saves £12 per month.
Where to compare apps: for users choosing a budgeting solution that connects to bank accounts, an independent roundup of personal finance apps can help weigh features and costs before linking accounts.
How To Get Started Safely: Step‑By‑Step Checklist For First‑Time Users
Start with verification: confirm the provider is authorised or licensed in the user’s country. That single step reduces the risk of sharing data with an unregulated app.
Step 1, Check licence and scope. Read the data access scope and purpose. A trustworthy app will list exactly which accounts and transaction ranges it needs.
Step 2, Use bank redirects. Always use the bank-redirect login flow so the app never asks for raw bank passwords. If an app asks for credentials directly, stop and do not continue.
Step 3, Inspect security details. Look for mentions of encryption, regulatory compliance (for example, PSD2 or local equivalents), and whether the provider uses OAuth or similar token-based systems.
Step 4, Limit permissions and time. Grant the minimum access needed and choose a shorter consent period when possible. If a tool only needs balance checks, don’t grant full transaction history for years.
Step 5, Monitor and revoke. Check the bank’s consent dashboard every 30–90 days and revoke any unused access. Also set account alerts for unusual transactions.
Practical honesty: the author recalls a case where a user granted broad access to test an app and later found two unexpected connections listed in their bank dashboard. That mistake cost an hour of cleanup and a small fraud alert, so the checklist emphasizes caution up front.
For related reading on everyday banking changes and secure mobile use, RarefiedTech offers a close look at digital banking changes and specific mobile wallet guidance that help users vet services before linking accounts.
Conclusion
Open banking gives people control: they choose who sees account data and for how long. The system reduces friction for payments and offers clearer financial views, but it requires cautious steps, verify providers, limit permissions, and monitor access. When a first-time user follows the checklist and prefers bank-redirect flows, open banking can save time and unlock services without exposing passwords or permanent access. RarefiedTech’s wider fintech coverage can guide the next decisions and tools a reader might try.